

— LAW ENFORCEMENT & GOVERNMENT
Cyber forensics & technical training
Built by the people who trained Israel's national cyber units.
From digital forensics to OSINT, from offensive understanding to ICS/SCADA — the same hands-on methodology, now available to European law enforcement and government organizations.
SINCE OCT. 2015 · TRUSTED BY GOVERNMENTS
— WHO IT'S FOR
Specialised training for the units that defend public institutions, citizens, and critical infrastructure.
// LAW ENFORCEMENT
Cybercrime investigation units
National police, regional forces, judicial police. Digital forensics, OSINT, network investigation, forensic evidence handling.
// GOVERNMENT & DEFENCE
Government and military cyber teams
National security agencies, military cyber units, government CERTs. Critical-infrastructure defence, threat hunting, national-scale incident response.
// INTELLIGENCE
Intelligence and counter-terrorism
Cyber intelligence units, counter-terrorism cyber teams. OSINT, threat-actor profiling, operational tradecraft on a controlled, air-gapped platform.
— TRACK RECORD
A decade of work with national agencies.
Not a launch event. A continuous record, in Israel and abroad, including a United Nations engagement. These are milestones, not the full list.
2016
A foreign government's national cyber programme.
Engaged to build a nation's cyber capability from the ground up — defence taught the only way that holds: by learning how an attacker operates, so you know exactly what you're protecting and where.
The same attack-to-defend method we still teach police and defence units today. This engagement is also where Cyberium itself was born — built to serve a nation-state, not in a lab.

2017
First Trust — the IDF and the Israeli Police.
The IDF adopted Cyberium for internal cyber-unit training — a seven-month intensive — and the Police followed.
Two of the most demanding training environments in the country, both on a platform barely a year old. The year the hands-on bet was validated.

2018 · UNITED NATIONS · MYANMAR
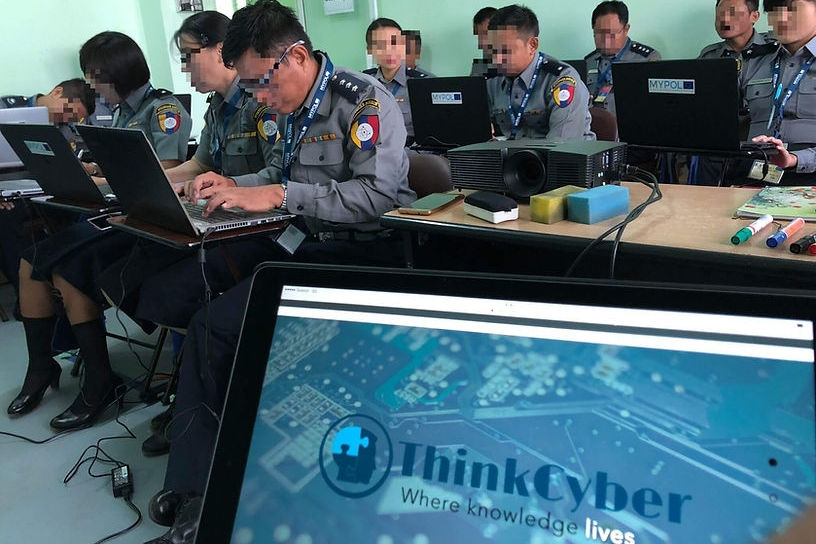
Training a foreign cyber force, under a UN programme.
ThinkCyber was brought into a United Nations initiative to strengthen Myanmar's national cybersecurity, tasked with training the country's cyber force in digital forensics — the skills to investigate and respond to complex threats. Proof that the method travels: a foreign government, a UN mandate, hands-on from day one.
2019 · IDF HOSHEN UNIT · SCADA CTF
A national defence challenge on a railway's control network.
More than 100 cyber soldiers, joined by the police's Lahav 433 unit and the Ministry of Public Security.
The mission: move from the IT network to the OT network, take control of the systems driving the trains, and save the passengers. It ran on Cyberium Arena.
Royalty Free Music: https://www.bensound.com · License code: 0PDU2HTEXHTNRNGK · Artist: Dollshade
2020 · FIRST RECORDED VIDEO LESSONS
From worldwide crisis to new capability.
When COVID closed the classrooms, ThinkCyber began recording its training sessions — and it changed the model for good. No more standing a whole unit down to sit in one room, on-site or over Zoom, all moving at one pace.
Agencies could now train self-paced: each officer learning on their own shift, at their own rhythm. The flexibility governments always needed, forced into being — and the way the platform still runs today.

2021
National Police Academy of Israel.
Immersive simulator sessions built into the academy's curriculum — new officers reaching the field cyber-ready.

2023 · NATIONAL CERT
Representing the State of Israel at Cybertech Africa.
Israel's national CERT adopted the platform for its advanced cyber training programme, and ThinkCyber presented the Profile · Train · Drill methodology at Cybertech Africa, in representation of the State of Israel.

2025 · NATIONAL CYBER DIRECTORATE (CERT-IL)
The national CERT trained its own SOC analysts on the platform.
Over two intensive days, more than 80 Tier-1 and Tier-2 analysts from the National Cyber Directorate — the body that defends the state's national networks — worked through the CERT-IL Advanced Cyber Course in SOC Digital Forensics and Incident Response: trace identification, network and malware investigation, and live incident scenarios, every exercise hands-on on Cyberium Arena.
When a national CERT puts its own front-line defenders through your platform — and issues a certificate of appreciation for it — the credibility question is settled.
Israel's National Cyber Directorate (CERT-IL) — SOC Digital Forensics & Incident Response course, certificate of appreciation.


2026 · TESDA · PHILIPPINES
A national government agency trains its own cyber team.
In October 2026, TESDA — the Philippine government's Technical Education and Skills Development Authority — put its own ICT team through a two-day hands-on workshop in Manila on Cyberium: network and traffic analysis, log investigation, scanning and malware concepts.
Not students — the agency's own people. Proof the work is current, and far from home.


Not where you'd expect. Even government and defence units begin with the Entry Bundle — the foundations plus one Level-3 program they choose. Because by Level 3, they already have working forensics, SOC or investigation capability in hand. From there, each unit builds the path its mission needs.
— THE TRAINING BEHIND IT
Where national agencies actually start.
Digital Forensics for Investigators
Evidence from computers and networks, for police and investigative teams.
-
Investigate Windows and Linux machines
-
Read network traffic, rebuild the timeline
-
Write findings someone else can follow
OSINT for Investigators
Find people and infrastructure from open sources, for intelligence units.
-
Research a target from public sources only
-
Connect what is found to the evidence
-
Hands-on, on real tools
Build a cyber unit, from zero
Take people with no background and finish with a working blue-and-red team.
-
Foundations together, then selection
-
Defenders and testers, trained side by side
-
A record of what each operator can do
Any path can be shortened, extended or combined. See the full catalogue →
— FOR YOUR NETWORK
See your network.
Train the people who defend it.
Specto+ shows an agency which machines are really on its network, which an attacker could reach, and what to fix first. It runs on the agency's own hardware, as one virtual machine — not a cloud service. For sensitive environments, nothing leaves until you decide where it goes.
The findings become training: the same real exposures become the scenarios your own analysts rehearse on.

1 VM
On your hardware.
On your network.
On your terms.
— METHODOLOGY
Profile. Train. Drill.
Training is built on the unit's profile, not a generic curriculum. Real terminals, real cases, scenarios drawn from real threat activity. Every module ends with a hands-on Lab Test; every program ends with its scenario — the final exam.
It is the same method ThinkCyber presented in representation of the State at Cybertech Africa.
9.6 / 10
rated by participants at a government workshop
Confidence in analysing a network rose from 4.2 to 7.3 out of 10 in the session.
— DELIVERY
From signature to first results.
The same steps every time, whether it is twenty officers or a national programme. Taught by our trainers, or by yours after we train them.
01 Your space
Your agency gets its own space on the platform, under your own name.
02 Your people
Send the participant list. Accounts and welcome emails go out.
03 Kick-off
A session shows participants the platform and what is expected of them.
04 Hands-on
Participants start the labs. The trainer follows every result on the dashboard.
05 The milestone
A workshop, a mission day or a CTF brings the unit together.
06 Report & next steps
A report on how the unit did, with options for what comes next.

Where a credential is needed, seven programs carry an optional City & Guilds Assured certification — a 140-year-old awarding body recognised by employers in over 80 countries. A watched, scenario-based exam on the same terminal the student trained on.